The Bugpocalypse Is Coming: AI Can Find Vulnerabilities Faster Than Humans Can Fix Them
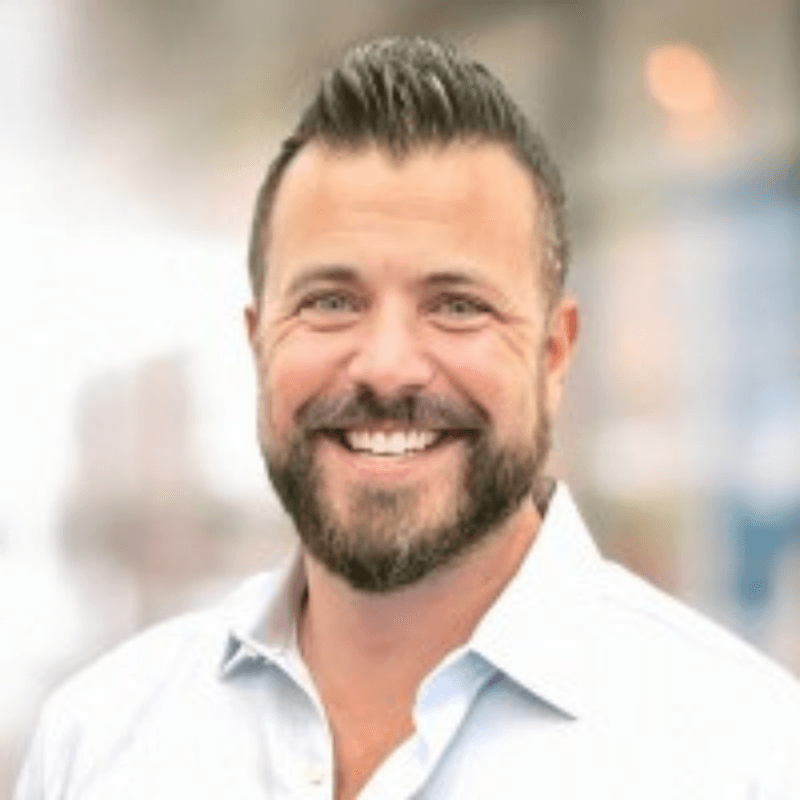
Trey Ford
Chief Strategy & Trust Officer, Bugcrowd
Most conversations about AI and cybersecurity focus on a simple question: will AI help defenders, or will it help attackers?
But that may be the wrong question entirely.
In this episode of the TPRM Podcast, Threats, Pitfalls & Risk Myths, Nate Lee sits down with Trey Ford, Chief Strategy & Trust Officer at Bugcrowd, former General Manager of Black Hat, former CISO of Deepwatch, and former security leader at Salesforce and Heroku.
The conversation explores what Trey calls the "Bugpocalypse" and why AI is fundamentally changing the economics of vulnerability discovery.
As AI dramatically lowers the cost of finding security flaws, organizations are entering a world where vulnerabilities can be discovered faster than ever before. The challenge is no longer simply finding problems. The challenge is validating them, prioritizing them, and deciding what to do when security teams are suddenly faced with thousands of findings and limited resources.
Nate and Trey discuss how bug bounty programs are evolving, why AI is accelerating both offensive and defensive security capabilities, and how organizations need to move beyond individual vulnerabilities and start thinking in systems.
They explore the future of software security, AI-assisted development, vulnerability management, technical debt, and why many organizations may need to rethink long-held assumptions about patching, remediation, and risk management.
The conversation also dives into AI governance, agentic systems, security operations, and the challenges security leaders face as every department begins adopting AI-powered tools faster than organizations can fully understand or govern them.
Trey shares lessons from decades of experience across consulting, vulnerability research, security leadership, and some of the industry's most influential organizations, offering practical insights into how security teams can adapt to a rapidly changing landscape.
This episode is essential listening for CISOs, security leaders, developers, risk practitioners, and anyone trying to understand how AI is reshaping cybersecurity.
About the guest
Trey Ford is Chief Strategy & Trust Officer at Bugcrowd.
Previously, Trey served as General Manager of Black Hat, Chief Information Security Officer at Deepwatch, and held security leadership roles at Salesforce and Heroku. He began his career as a security consultant and PCI assessor and has spent decades helping organizations understand and manage cyber risk.
His work spans vulnerability research, security operations, product security, bug bounty programs, governance, and cybersecurity strategy.