AI is accelerating cyberattacks to machine speed. But most security programs were built for a world where attackers moved at human speed.
What happens when an attacker can move through an environment in seconds, security alerts keep multiplying, and hiring more analysts is no longer enough?
In this episode of the TPRM Podcast: Threats, Pitfalls & Risk Myths, Nate Lee sits down with Mandy Andress, Chief Information Security Officer at Elastic, to explore how artificial intelligence is changing the economics, operations, and strategy of cybersecurity.
Together they examine how AI is accelerating existing attack techniques, why traditional security programs struggle to operate at machine speed, and how security leaders can redesign their approach to risk, detection, and response.
Mandy shares how Elastic is applying AI and agentic workflows to its security operations, including an experiment in which a multi-agent approach to automated alert triage proved five times less expensive than a single-agent approach.
But efficiency is only part of the equation.
As organizations adopt AI, security teams must balance detection quality, token consumption, operational costs, and human judgment. Mandy explains why adding more people won't solve the growing volume of security alerts, and why the next generation of security programs will need to rethink how they allocate resources.
The conversation also explores how attackers are using AI to accelerate lateral movement, why traditional approaches to prevention need to evolve, and how security leaders can communicate risk in ways that resonate with business executives.
The conversation covers
- Why AI is accelerating cyberattacks to machine speed
- How attackers can use AI agents to accelerate lateral movement after gaining access
- Why hiring more security analysts won't solve the growing volume of alerts
- How Elastic reduced automated alert triage costs by 5X using a multi-agent approach
- The economics of AI security, including token costs, detection quality, and operational efficiency
- Why prevention, least privilege, and limiting the blast radius matter in an AI-driven environment
- How red team exercises help organizations identify and prioritize real business risks
- The changing role of human judgment in security operations
- Why curiosity, critical thinking, and adaptability remain essential cybersecurity skills
- How AI could transform governance, risk, compliance, and continuous risk assessment
Mandy also shares how Elastic has experienced a more than 100-fold increase in bug bounty submissions over approximately nine to ten months, illustrating the scale of the operational challenges security teams are beginning to face.
Drawing on her background in accounting, technology, auditing, and law, she offers a business-focused perspective on building security programs that can adapt to rapidly changing technology without losing sight of cost, effectiveness, and organizational priorities.
Whether you're a CISO, security engineer, SOC analyst, technology executive, or business leader navigating AI adoption, this conversation offers practical insights into how security programs can evolve to meet the challenges of an increasingly automated world.
About the guest
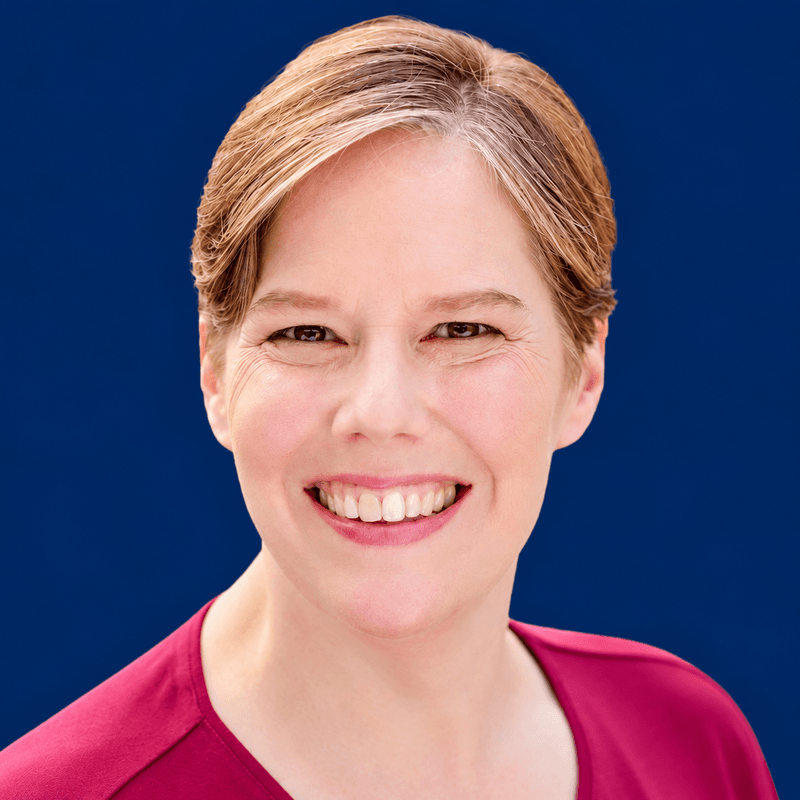
Mandy Andress is Chief Information Security Officer at Elastic. Her career spans accounting, systems auditing, security consulting, architecture, and enterprise security leadership. She also holds a law degree, bringing a multidisciplinary perspective to cybersecurity, risk management, governance, and regulatory requirements. At Elastic, she leads security efforts in an environment where AI and agentic technologies are reshaping both the threats organizations face and the tools available to defend against them.